NSAA SECURITY · SBB Assurance LibraryFrameworks and scope
ISO/IEC 27001:2022, NIST CSF 2.0 and IRAP/ISM—distinct frameworks with different assurance semantics.
Three framework records
For each record, inspect scope, evidence type, assessment authority and time context. A review due date is not always a certificate expiry date.
- ISO 27001 can support a certificate-status question only if a genuine in-scope accredited certificate exists.
- NIST CSF alignment does not create a NIST-issued certificate.
- IRAP is a review of system security by an endorsed individual, not a certification scheme.
Reading the dates
Prepared: When the illustrative record was composed.
Next review: Suggested review checkpoint.
Expiry: Applicable only if a genuine document explicitly provides one and its issuer is verified.
ISO/IEC 27001:2022
ISO/IEC 27001 is a certifiable information security management system standard. This illustrative record is not evidence that NSAA Security holds an accredited certification. A positive determination requires independently verifiable certificate details, an accredited certification body and the exact scope.
Example scope: NSAA Security consulting, cloud security advisory and third-party risk services
Prepared: 14 July 2026
Review: 13 July 2027
Issuer/authority: No issuer verified
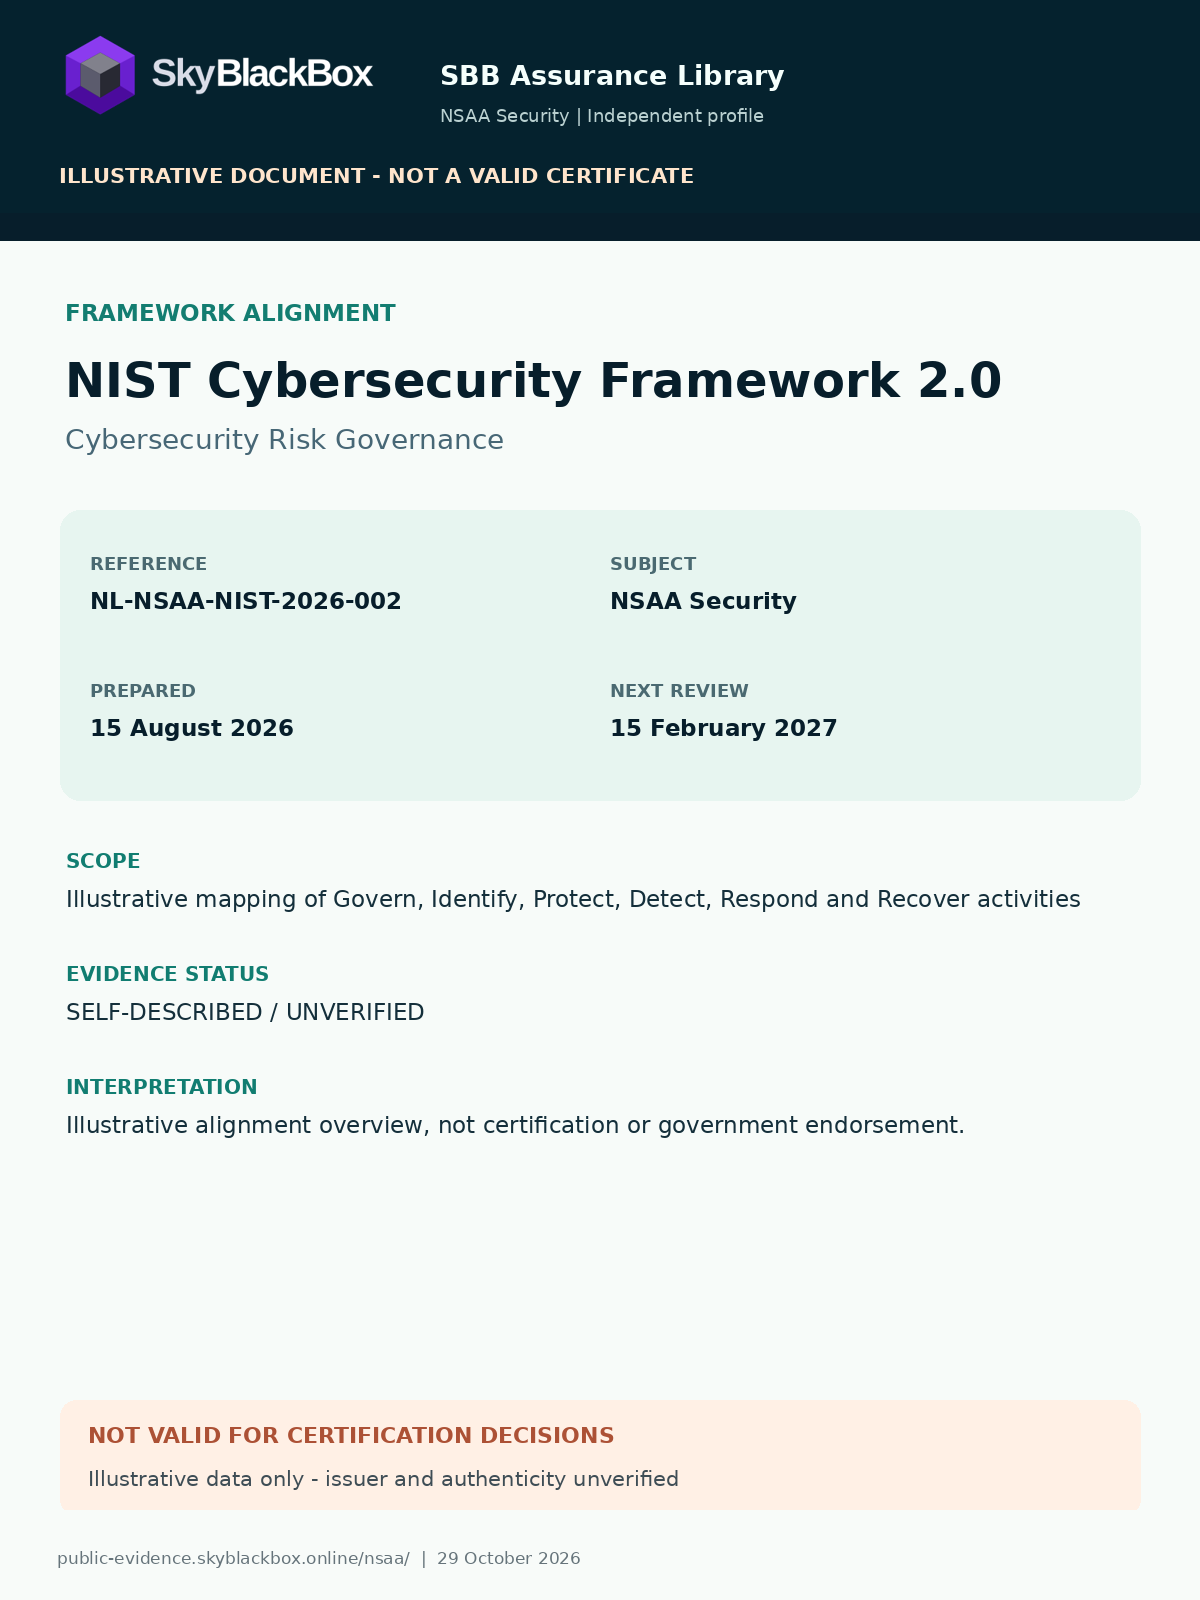
Framework alignmentNIST Cybersecurity Framework 2.0
NIST does not certify or endorse Cybersecurity Framework implementations. The six CSF 2.0 functions describe a useful governance structure, but a framework mapping alone does not prove that any control is operating effectively.
Example scope: Illustrative mapping of Govern, Identify, Protect, Detect, Respond and Recover activities
Prepared: 15 August 2026
Review: 15 February 2027
Issuer/authority: No NIST certification exists
Assessment scope noteIRAP / Australian ISM
IRAP is a program of endorsed individual security assessors. An IRAP assessment is not a certificate or ASD accreditation. A relying organisation must review the completed assessment report, its scope, findings and applicable risk acceptance authority.
Example scope: Hypothetical cloud service security boundary and selected Australian ISM controls
Prepared: 20 September 2026
Review: 20 March 2027
Issuer/authority: No assessor identified